
Gootloader and Law Firms: What the FBI's New Alert Means
Gootloader and law firms: the FBI's November 16, 2026 FLASH alert names attorneys as targets. How the SEO poisoning works, and what to check this week.
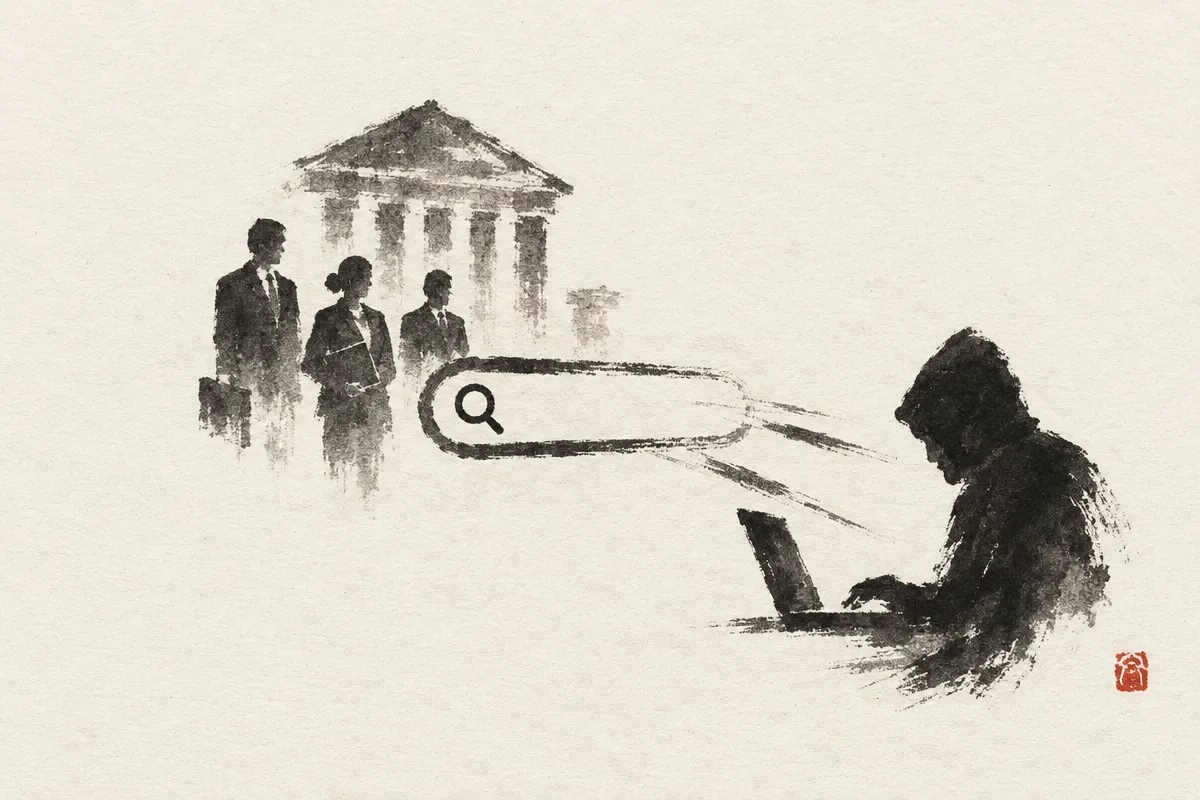
Gootloader and law firms are now a documented pairing. On November 16, 2026, the FBI released a FLASH alert describing a long-running malware campaign that hijacks WordPress websites and manipulates search results to reach people hunting for legal documents. In 2025 and 2026, the people it hunted were lawyers. Your firm’s website is the other half of the problem. If it runs WordPress, it can be turned into the delivery vehicle for the attack rather than only a target of it.
I have spent 25 years in software engineering and digital marketing, and most of my work today is building and marketing websites for law firms. I am not a lawyer. This is not legal advice. The alert lands exactly where my work lives, though, on law firm websites and their search visibility. Here is what it says, and what I would do this week.
Gootloader and Law Firms: Why This Is Urgent Right Now
This is not an old story resurfacing. Five facts from the alert make it worth acting on.
- The alert is brand new. The FBI released it on November 16, 2026.
- The targets were legal professionals. In 2025 and 2026, the FBI says the poisoned search terms were aimed at practicing attorneys, in-house counsel, law firm partners, litigation and privacy teams, legal operations staff, general counsel and legal technology decision makers.
- The newest phase abuses WordPress comment paths. From 2025 onward, the campaign added comment-path abuse and geofencing, so the malicious content is served only to visitors from certain locations.
- You may already be infected and not know it. Poisoned content is often shown only to search engine crawlers. Your site looks completely normal to everyone in your office while Google indexes attack pages on it.
- The money is real. The FBI ties this campaign to more than $28 million in ransomware payments.
Is this a WordPress problem or a law firm problem? Both, and the overlap is enormous. When I ran Google’s speed test on 421 South Florida law firm websites this year, at least 70% of them turned out to be running WordPress. That is the sector’s default stack. It is also Gootloader’s.
One update the alert does not resolve for you. Between November 9 and November 11, 2026, Europol and partner agencies seized Gootloader servers and domains in a coordinated action (BleepingComputer). Good news. It does not shorten your to-do list, because seizing a server does not patch a hacked WordPress install and it does not expire the credentials already stolen from one. The FBI published its hardening guidance five days after that takedown. Draw your own conclusion about how much cleanup is still sitting with site owners.
What the FBI Alert Says
The alert is FBI FLASH CC-111626-MW, coordinated with CISA. It went out as TLP:CLEAR, which means it is meant to be shared. Its title is “Gootloader Malware Using SEO Poisoning and Compromised Websites to Gain Initial Access.” You can read the full alert on IC3.gov.
The FBI describes Gootloader as an initial access framework built from a JavaScript loader and a network of compromised websites. SEO is how it finds victims. Attackers use the framework to get a foothold inside an organization, and that foothold is often the first step toward a ransomware attack.
The scale, as of October 2026
- Activity observed from 2020 through 2026, across many sectors
- More than 1,000 infected WordPress sites
- 216 domains controlled by the Gootloader administrator
- More than $28 million in ransomware payments
Search Engine Roundtable covered the alert too, if you want a shorter summary: FBI Says SEO Poisoning Led To $28 Million In Ransomware Payments.
How the Attack Works, Step by Step
Here is the attack in plain language, based on what the FBI describes.
- They find a way in. Attackers scan for WordPress sites with an exposed
xmlrpc.phpfile, then brute force the login or use stolen passwords. - They take over the site. They abuse outdated plugins and themes, inject posts, misuse XML-RPC and REST routes, and modify the site’s JavaScript. Plugins are where this ecosystem bleeds. Patchstack counted 11,334 new WordPress vulnerabilities in 2025. Ninety-one percent of them were in plugins. Six were in core. The weighted median time from public disclosure to first exploitation was five hours (Patchstack, State of WordPress Security in 2026). I went through what that cadence costs a firm in the plugin tax piece.
- They make their lure pages rank. Hidden keyword links and arranged backlinks push those pages up for low-competition legal searches, like a jurisdiction-specific contract clause. The result sits next to legitimate legal resources.
- They decide who sees what. A traffic filter sorts visitors by country, referrer, cookie or IP address. Crawlers get the poisoned content. The site owner gets a normal site.
- Someone clicks. A searcher, often a lawyer, clicks what looks like an ordinary result and downloads what looks like a template. That download is the loader.
Why the lure is harder to catch than it sounds
Two details from independent researchers matter here. Huntress found injected JavaScript posting to WordPress’s own comment endpoint, /wp-comments-post.php, to deliver the payload, along with a custom WOFF2 font that disguises the filename in the page source (Huntress). The ZIP archive the victim downloads is deliberately malformed, so Windows opens it happily while many security and analysis tools cannot (Security Affairs). Nothing about the click feels wrong.
What Happens After the Download
Gootloader is not the ransomware. It is the thing that sells your door open to whoever wants it. That distinction explains why the damage ends up so far out of proportion to one careless download.
The loader checks the room first
The ZIP contains a JScript file. Windows runs it. In the versions researchers have documented, the loader only proceeds with full payload delivery on machines joined to an Active Directory domain, which is to say on real office networks rather than a researcher’s laptop. It writes later-stage scripts into the AppData directory under harmless extensions and stores payload blobs in the HKEY_CURRENT_USER registry hive (MITRE ATT&CK S1138).
Then it is hands on keyboard
Gootloader has historically delivered Cobalt Strike and ransomware families including REvil, and the 2025 resurgence has been tied to Vanilla Tempest and Rhysida. In one intrusion Huntress tracked, the attackers reached a domain controller 17 hours after initial access (The Register, November 6, 2025). Seventeen hours. That is one overnight.
Why the encryption is unrecoverable
The encryption step itself is unglamorous math. Modern ransomware generates an AES key to encrypt your files, then wraps that key with the attackers’ RSA public key, which is what makes recovery without their private key computationally unrealistic (Vectra AI). Before any of that, most crews copy the data out and threaten to publish it. That is double extortion, the dominant model since about 2020 (Vectra AI). For a firm holding privileged client files, the copy is the part that should worry you more than the downtime.
Why Gootloader Targets Law Firms Specifically
The question I hear is short. Why us? There are two answers, and they run in opposite directions: your people can be hit through search, and your website can be conscripted to hit someone else’s.
The search side
Legal searches are low competition and high intent. Very few websites compete for one contract clause in one state. A lure page needs almost no help to rank there. And the person searching genuinely wants to download a document, so the click is already decided before they even see the result.
Downloading templates is normal work. Attorneys and staff pull sample agreements and forms every day. One more file from a search result looks like nothing at all.
The website side
A lot of law firm sites are easy to break into. Plenty of the firm websites I look at run an aging WordPress install with an unprotected xmlrpc.php and plugins nobody has touched in two years. That is the door Gootloader knocks on.
Law firms make good ransom targets. Confidential client files and deadlines that do not move. That is the combination that makes a demand work.
The damage also compounds before anyone notices. There is usually a long window between the compromise and the discovery, and during that window your own site is serving malware to its own visitors. Here is my SEO read, and it is my opinion rather than an FBI claim: a hacked site also passes its link authority to the attacker’s lure pages, which is part of why those pages rank at all. Removing the malware takes an afternoon. Rebuilding the firm’s standing with Google takes a great deal longer.
What to Do Now
The checklist
The FBI gives site owners a clear set of recommendations. Hand this to whoever manages your website.
- Update WordPress core. Update every plugin and theme, then delete the ones you are not using.
- Turn on phishing-resistant multifactor authentication for every WordPress admin account and for your hosting account.
- Disable
xmlrpc.phpif you do not need it. If you do need it, rate-limit it and allow only the methods you actually use. - Run PHP as a non-privileged account and deny PHP execution under
wp-content/uploads. - Compare your WordPress core files against the official checksums to spot modified files.
- Check Google Search Console for search queries unrelated to your practice, especially legal or business phrases you never wrote about, and for sudden jumps in newly indexed pages.
Do that last one today. Because the poisoned content is often served only to crawlers, Search Console may be the only mirror you have. If a personal injury firm is suddenly collecting impressions for contract clauses from another state, treat it as a finding rather than a curiosity. I am using personal injury as an illustration here, not reporting a matter I worked on.
Who holds your logins
One practical obstacle. If your vendor holds the hosting panel and the WordPress admin logins, you cannot work this list and you cannot verify that anyone else did. That is a governance problem before it is a security problem, and I have argued it at length in why your firm should own every account.
If You Think Your Site Was Already Hacked
If something looks wrong, the FBI recommends these steps.
- Put the site into a maintenance or restricted state, but preserve a forensic copy first: files, database, logs and hosting configuration. Do not wipe the evidence.
- From a clean computer, reset every credential tied to the site: hosting panel, SSH, SFTP, WordPress admin, database, API keys and CDN. Revoke active sessions and application passwords.
- Identify how the attackers got in. Restore from a known-clean backup only after you have removed that vulnerability or stolen credential. Otherwise they walk right back in.
- Contact the FBI.
Call your website vendor and ask directly whether they have checked for this. No vendor? Bring in someone who does WordPress incident response.
Why I Build Law Firm Sites on Nova
This is my perspective, and I have a stake in it. I build law firm websites on Nova DT, my own platform, and alerts like this one are a big reason why.
Look again at the attack path the FBI describes. Brute-forcing xmlrpc.php. Exploiting vulnerable plugins. Misusing WordPress REST routes. Dropping PHP into the uploads folder. Nearly every step of it depends on the WordPress ecosystem.
Nova is not WordPress, so that specific attack surface is not there:
- No plugins to patch. There is no third-party plugin or theme ecosystem to fall behind on, and no abandoned plugin quietly sitting on your server waiting to be exploited.
- No
xmlrpc.phpendpoint. The front door Gootloader most often knocks on does not exist. - No PHP uploads folder. There is no
wp-content/uploadsdirectory where an attacker can drop and run a script. - No comment endpoint to hijack. The
/wp-comments-post.phppath Huntress watched deliver payloads is not part of the stack.
Security is not the only reason I use it. Nova sites are fast and ADA compliant. They are also built to be read by AI search tools as well as by Google, which is a question of architecture rather than a question of how much content you publish, and I made that case in machine-first architecture for law firm websites. With some training, your team can manage the site yourselves.
To be clear, no platform is immune. A smaller attack surface lowers risk. It does not remove it. Stolen passwords still work on any system, which is why unique passwords and multifactor authentication on every account matter no matter what your site runs on. But I would rather my clients spend their attention there than on a monthly plugin update cycle.
Next Steps
If your firm’s website runs on WordPress, work the checklist this week. Start with Search Console. If you want a second set of eyes on your site, or you want to talk about whether Nova makes sense for your firm, write me at hi@carlosarias.com.

I'm a Marketing Engineer specializing in digital marketing for law firms, helping firms turn online visibility into signed cases. I work directly with a select group of firms on SEO and local search, website conversion, lead intake and follow-up, CRM automation and marketing analytics.
Continue reading
The Rise of Agentic Websites: Why Law Firm Sites Are Becoming Autonomous
The rise of agentic websites is turning law firm sites from static brochures into autonomous systems that research, publish, and convert. Here is how.
SEO for Personal Injury Lawyers: What Signs Cases in 2026
SEO for personal injury lawyers, measured in signed cases: what a small PI firm can take from TV budgets, what it costs, how long it takes.
95% of South Florida Law Firm Websites Have the Errors Behind ADA Lawsuits
We scanned 105 South Florida law firm websites for the accessibility errors cited in ADA website lawsuits. 98 of the 103 we could scan had at least one.